
HugeGuard Cloud
HugeGuard Cloud: cloud DDoS protection
Protect your network with Huge’s mitigation infrastructure. Plan integration with our team and monitor service resources through HugeCP.

Mitigation flow
Traffic flow through the mitigation network
- InternetInbound traffic
- Huge networkAnalysis and mitigation
- Protected environmentValidated traffic
- Aggregate capacity
- 30 Tbps
- Across the platform
- Mitigation centers
- 15+
- Across the network
- Availability
- SLA
- As defined by the contracted service
- Automatic detection time
- <5 s
- For integrated networks
Why choose cloud protection?
The cloud option provides distributed mitigation without a local appliance.
Anycast IP Backbone
Distributed PoPs to absorb attacks close to the source
Automatic detection
Detection applies to integrated networks; mitigation start depends on the attack vector, configuration and contracted service.
Always-On Protection
In-line protection and mitigation according to the contracted service.
Zero Hardware
Cloud solution without a local appliance.
HugeGuard Cloud
How does cloud DDoS protection work?
Our architecture combines defense layers to address different types of DDoS attacks.
- 1
Anycast Interception
Traffic is captured at the edge of the global network before reaching the destination
Our anycast network distributes traffic across multiple strategically positioned PoPs (Points of Presence), absorbing attacks close to the source and reducing latency.
- 2
Behavioral Analysis / Baselines
AI analyzes traffic patterns in real-time to identify anomalies
Analysis identifies suspicious patterns and volume changes to guide mitigation policies.
- 3
Multi-Layer Mitigation
Application of filters at layers 3, 4 and 7 of the OSI model
Blocking volumetric (L3/L4) and application (L7) attacks through rate limiting, blacklisting, whitelisting and adaptive behavioral filters.
- 4
Traffic delivered via VPN or Fiber/Interconnection
Only legitimate traffic is forwarded to your infrastructure
Validated traffic is delivered via VPN tunnel or direct interconnection.
Complete protection for your entire infrastructure
Web Application Protection
Protect websites and APIs against application layer attacks
- HTTP flood protection
- Bot attack mitigation
- Intelligent rate limiting
- Integrated WAF
Infrastructure Protection
Defend your network against volumetric and protocol attacks
- UDP/TCP flood protection
- SYN flood mitigation
- ICMP flood defense
- Amplification attack filtering
DNS Protection
Keep your DNS services always available
- DNS flood protection
- NXDOMAIN attack defense
- Cache poisoning prevention
- Resilient Anycast DNS
Advanced Features
Intelligence and automation against threats
Our platform uses machine learning and behavioral analysis to identify and block even the most sophisticated attacks.
Behavioral Analysis
Identifies anomalous patterns and zero-day attacks
Adaptive Rate Limiting
Dynamically adjusts limits based on behavior
Multi-Layer Protection
Defense in depth at layers 3, 4 and 7
Real-Time Analytics
Complete dashboard with detailed metrics and insights
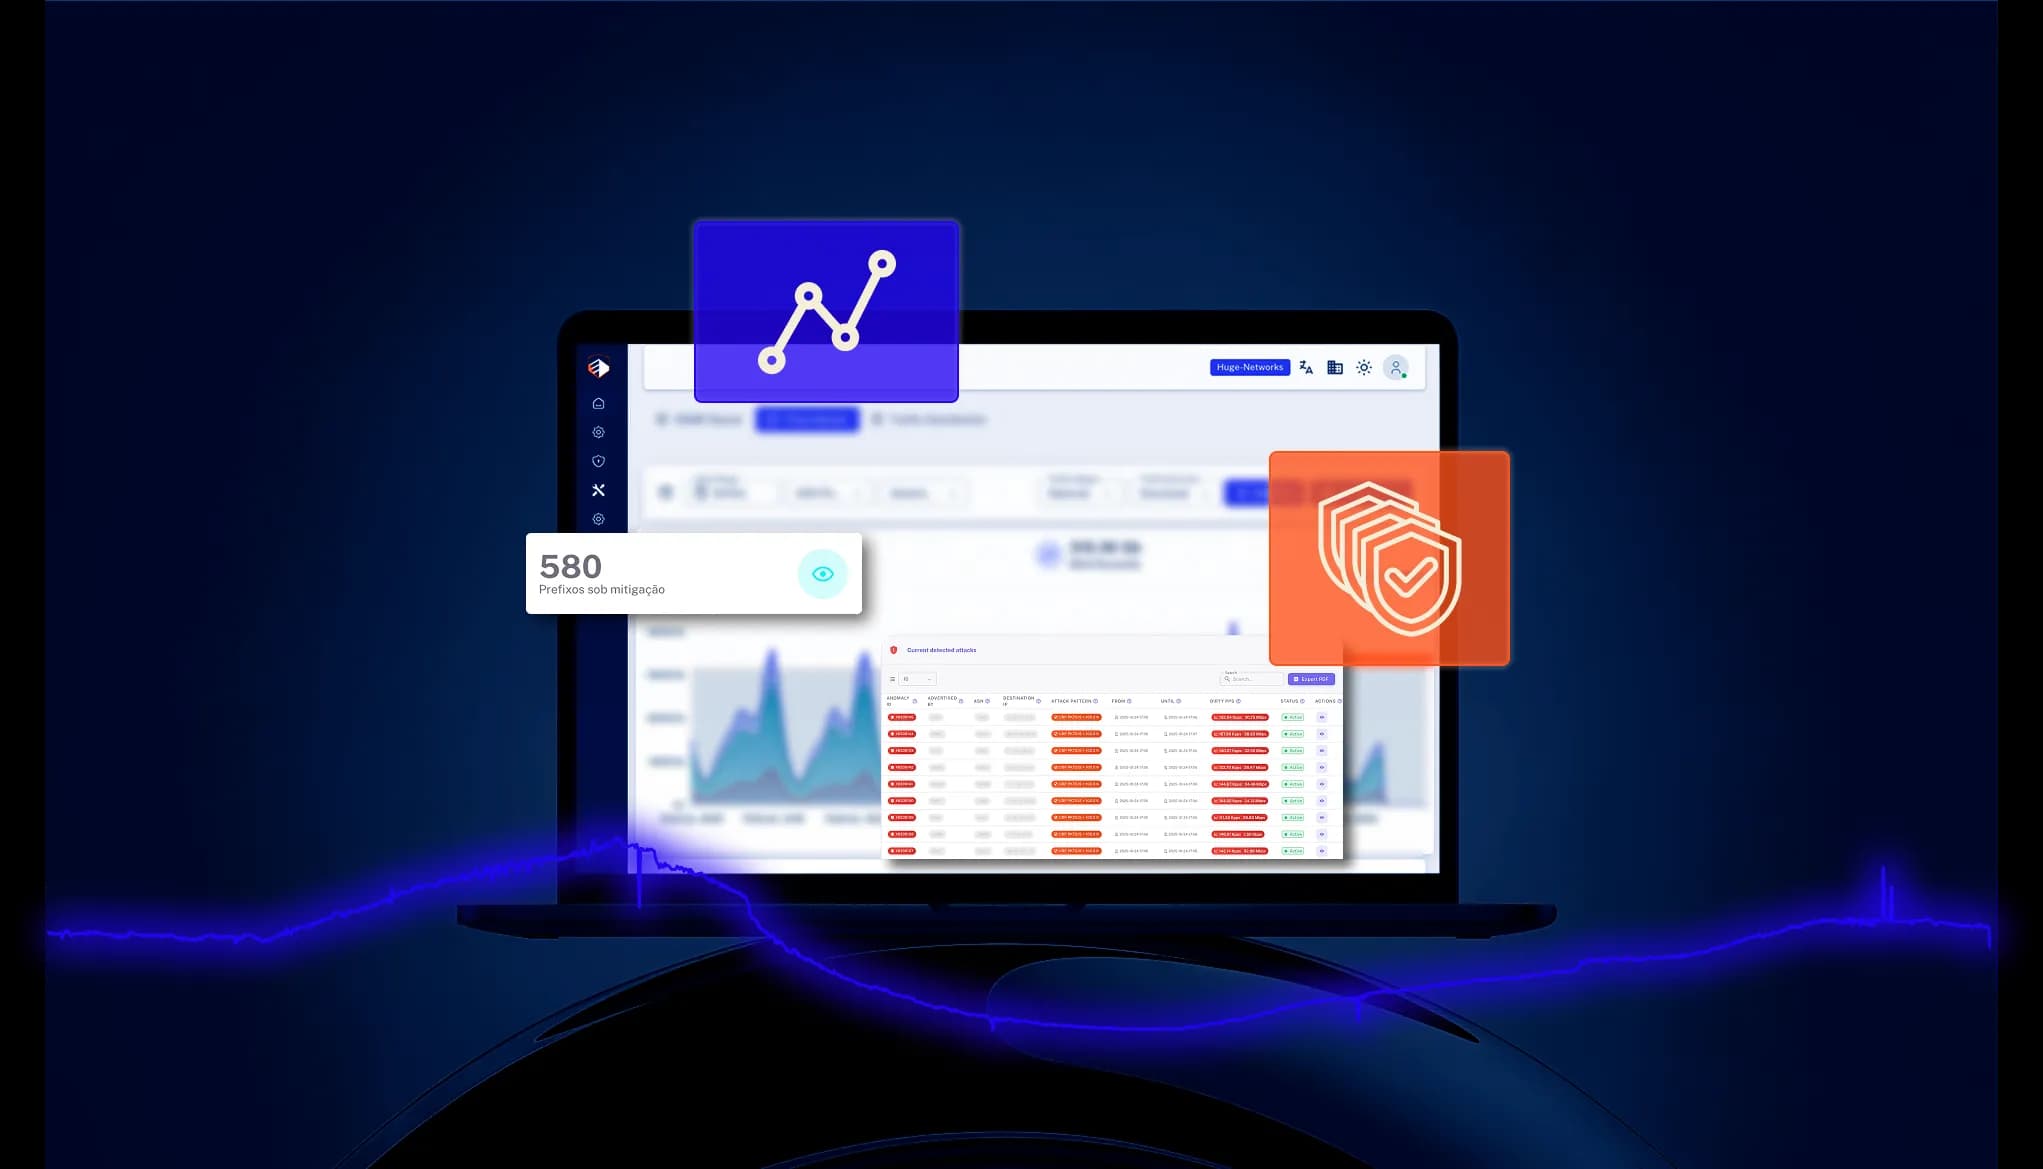
HugeCP included
Monitor protection. Understand what happens on your network.
The portal is part of your contracted services. Your team gains a place to investigate traffic and review available protection resources.
Visibility for investigation
Review traffic and anomalies within your company’s scope to identify where to investigate further.
Defined policies and access
Review protection policies and use the controls enabled for your team’s roles.
Context to follow operations
Review available events and history to support analysis and communication with Huge operations.
Resources and controls vary by service, configuration and permissions. The Huge team will explain the scope available to your operation.
Simple and fast integration
Integration method and timing depend on technical assessment; the cloud solution does not require a local appliance.
Web Application Protection
DNS integration for websites and APIs
DNS Pointing
Point your domain’s A/AAAA records to the Huge anycast protection network.
SSL Configuration
Configure SSL/TLS with your certificate or the available free option to secure communication with users.
Active Protection
After configuration is validated, traffic is monitored and protected according to the contracted service.
Infrastructure Protection
BGP integration for networks and autonomous systems
Connection Establishment
Connect your network to Huge through a VPN, dedicated L2 link or cross-connect.
BGP Session Configuration
Configure the GRE tunnel and establish the BGP session to exchange routing information with the protection network.
IPv4/IPv6 Announcements
Announce your IPv4/IPv6 prefixes over BGP so the Huge network can route and protect your traffic.
Server Protection
Proxy integration for servers and applications
Proxy Configuration
Configure the reverse proxy to route HTTP/HTTPS traffic from your servers through the protection network.
SSL Certificate
Configure SSL/TLS certificates, with termination on the Huge network or shared certificates.
Active Protection
Protect servers through the proxy against layer 7 and volumetric attacks, according to the contracted configuration.
Need local filtering or hybrid protection?
Let's talk?
Our team of specialists is ready to help you protect your infrastructure.
Cloud solution with an anycast network. No local appliance; integration options and protection scope are defined after technical assessment.
Zero Hardware
100% cloud solution without the need for local equipment
Integration assessment
Method and timing are defined after technical assessment, via DNS, BGP or reverse proxy.
Global Anycast Network
15+ PoPs distributed globally to absorb attacks close to the source
Always-On Protection
24/7 monitoring and automatic mitigation according to the contracted service.
Request a personalized proposal
All fields are required.